Docs
Identity, offerings, and how security and cyber teams run Eridas — then the Cloud API, TypeScript SDK, CLI, and MCP. Same contracts for humans, CI, and agents.
Identity
What Erydas is
Erydas is open-source, deterministic dependency security and cyber defense for npm, live web apps, and AI-assisted teams. We read exact versions from package-lock.json, match them to disclosed OSV advisories (CVEs, GHSAs, and MAL malware records), scan live URLs passively, and apply the smallest verified direct-dependency update — or we change nothing. Advisory truth is 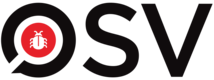 . Optional AI can explain a confirmed finding. It never invents a vulnerability and never picks a version. The same scanner, live-edge recon engine, and fix planner run in the CLI, Cloud dashboard, API, SDK, MCP, and CI.
01
OSV is truth
Disclosed advisories from OSV decide what is vulnerable — including CVE, GHSA, and MAL malware IDs. Erydas never scrapes forums, guesses CVEs, or lets a model invent findings.
02
The lockfile is inventory
Exact installed versions in package-lock.json decide what is in the tree. A stale lockfile is an error, not a guess.
03
Mutation is gated
Fixes are planned, approved, applied with lifecycle scripts disabled (--ignore-scripts), rescanned, and rolled back together if verification fails.
Surfaces
What we offer
One deterministic pipeline, every surface your stack touches. Solo engineers, security teams, CI, and coding agents share the same contracts.
CLI
Open-source npm package
eridas scan, fix, init, and tinfoil. Zero account required. Same deterministic planner Cloud uses under the hood — any laptop, CI runner, or agent sandbox.
CommandsCloud
GitHub App and command center
Connect an org once. Security posture overview, Guided and Dev UIs, queued scans, findings, and fix PRs on a dedicated branch. Never merges to default.
Open CloudLive app
Leveled passive site recon
GET-only scan of any public URL: L1 surface, L2 exposure, L3 supply chain, L4 reconstruction. One report, a grade per level, in under a minute.
Levels guideAPI & SDK
Headless /api/v1 & /api/v2
Typed TypeScript client (@eridas/cloud-sdk) for scans, findings, remediations, investigations, repo sync, and long-poll wait. Stable JSON for SOAR and tickets.
DocsAgents
MCP, SKILL.md, and llms.txt
Native @eridas/mcp server for Cursor and editors, portable SKILL.md for Claude Code and Codex, and machine docs. Same flags, exit codes, and dry-run path as CI.
For agentsCI
Scheduled GitHub Actions
eridas init writes a pinned workflow. Scan mode requests contents:read only. Fix mode opens or updates one reviewable PR on eridas/automated-remediation.
Team runbook
Operators
How security and cyber teams run it
Start read-only. Gate CI on exit codes. Scan the live app. Connect GitHub when you are ready for pull-request remediation — never a push to default.
- 01
Baseline the lockfile (read-only)
Inventory exact installed versions against OSV. Use JSON in pipelines. Exit 1 means disclosed findings remain at your threshold — do not treat the tree as clean.
npx eridas scan . --quiet --format json - 02
Schedule a read-only watch
Generate eridas.config.json and a GitHub Actions workflow with contents:read only. Keep this mode until you trust PR-based remediation.
npx eridas init . --mode scan - 03
Scan the live product
Level 2 (default) covers exposure: headers, leaked .env/.git/source maps, secrets in bundles, public API docs. Level 3 adds the OSV supply-chain check. Scans are passive and refuse private addresses.
npx eridas tinfoil https://example.com --level 2 - 04
Connect GitHub for the org
Sign in to Erydas Cloud, install the GitHub App, create an erd_ API key. Store keys in CI secrets or local env — never in eridas.config.json. GitHub-gated endpoints return 403 until the App is installed.
eridas auth login - 05
Remediate on a pull request
Promote to init --mode fix or open a Cloud remediation. Fixes land on eridas/automated-remediation for normal branch protection. --force skips the prompt only — not rescan, verification, rollback, or major policy.
npx eridas init . --mode fix - 06
Pin policy and prove the fix
Keep allowMajor false until you opt in. Set verificationCommands (npm test, lint, typecheck). Pin the Erydas version in the generated workflow. Gate CI on exit codes 0/1/2/3.
npx eridas fix . --dry-run --quiet --format json
Full policy, exit codes, and the operator checklist live in the security team runbook · security model.
Open-source vs Cloud
- npm / CLI — local scan and fix, no account.
npx eridas scan . - Eridas Cloud — GitHub App, dashboard, API keys, remote scans and fix PRs when your account is connected.
Markdown sources live in the repo under docs/. The team runbook is For security and cyber teams.
Authentication
Authorization: Bearer erd_…Create a key in the dashboard. CLI: eridas auth login. SDK: new EridasCloudClient({ apiKey }).
GitHub-gated endpoints return 403 github_not_connected until the GitHub App is installed for the org.
TypeScript SDK
import { EridasCloudClient } from "@eridas/cloud-sdk";

const client = new EridasCloudClient({
  apiKey: process.env.ERIDAS_API_KEY!,
  baseUrl: process.env.ERIDAS_API_URL ?? "https://erydas.vercel.app",
});

const me = await client.me();
const { repos } = await client.listRepos();
await client.scanAndWait({ repoId: repos[0]!.id });
CLI + curl
eridas auth login --api-key erd_… --api-url https://erydas.vercel.app
eridas cloud repos --format json

curl -s https://erydas.vercel.app/api/v1/me \
  -H "Authorization: Bearer erd_…"
Endpoints
POST /api/v1/tinfoil
Scan a live app by level (each level includes the ones below) and get one graded report. Returns { id, result }; with stream: true it sends NDJSON step, result and error events. Same report as the Scan page, `eridas tinfoil` and MCP.
{ "url?": "https://example.com", "level?": 1 | 2 | 3 | 4, "packages?": ["lodash@4.17.20"], "lockfile?": "<package-lock.json text>", "repoId?": "<uuid>", "stream?": true }GET /api/v1/tinfoil
Recent site scans for the org
GET /api/v1/tinfoil/:id
One saved scan: { id, createdAt, level, target, result }. The Scan page permalink is /scan?scan=<id>.
GET /api/v1/me
Org, actor, GitHub connection status, and capabilities
GET /api/v1/repos
List connected repositories
GET /api/v1/repos/:id
Get a single repository (includes package-root / stack)
POST /api/v1/repos/sync
Re-sync repos from the GitHub App (requires GitHub connected)
GET /api/v1/repos/:id/git-status
Git/PR worktree status (requires GitHub connected)
GET /api/v1/repos/:id/package-root
Detect package roots / stack (requires GitHub connected)
PATCH /api/v1/repos/:id/package-root
Set npm package directory (requires GitHub connected)
{ "packageRoot": "apps/web" }POST /api/v1/scans
Queue an OSV scan for a repository
{ "repoId": "<uuid>", "skipUnchanged?": true }GET /api/v1/scans/:id
Get scan status (?wait=true&timeoutMs=20000 to long-poll)
GET /api/v1/findings?repoId=<uuid>
List findings for a repository
POST /api/v1/remediations
Open a fix PR — all packages, one package, or one advisory
{ "repoId": "<uuid>", "packageName?": "vite", "osvId?": "GHSA-…" }GET /api/v1/remediations/:id
Get remediation status and PR URL (?wait=true supported)